
Trust centre
Security and compliance
African Payment Solutions is a PCI DSS Level 1 compliant service provider - fully compliant at the standard's highest level. This trust centre is the one page procurement and security teams need: our compliance status, how we handle data, our POPIA commitments, live platform status and how to request the full compliance pack.
Compliance at the standard's highest level
PCI DSS Level 1 is the most stringent tier of the Payment Card Industry Data Security Standard - the tier required of providers processing the highest transaction volumes, validated through independent on-site assessment rather than a self-assessment questionnaire. African Payment Solutions is a PCI DSS Level 1 compliant service provider - fully compliant at the standard's highest level. For merchants, the practical meaning is that the heaviest compliance burden sits with us: use hosted checkout and card data never touches your servers, which keeps your own PCI scope at its minimum.
How is data protected?
We publish our data-handling principles at category level and keep implementation detail where it belongs - in documentation shared under NDA.
- Tokenisation. Card numbers are exchanged for tokens on arrival and stored in an isolated vault. Everything downstream - merchant systems, reporting, recurring billing - works with tokens, not card numbers.
- Encryption everywhere. Data is encrypted in transit and encrypted at rest, without exception.
- Key management. Encryption keys are held in cloud HSM-backed key management within AWS managed services, with access controlled and audited.
We deliberately do not publish service names, network topology or infrastructure detail on a public page; security teams who need that depth can request it with the compliance pack.
POPIA, in plain language
POPIA - the Protection of Personal Information Act - is South Africa's data protection law, and our processes are aligned with it. We collect the minimum personal information required to process payments, run compliance checks and meet our legal obligations. We use it only for those purposes. We protect it with the same controls that protect cardholder data. We do not sell it, and we support merchants in meeting their own POPIA obligations for the payment data we process on their behalf.
What availability does the platform deliver?
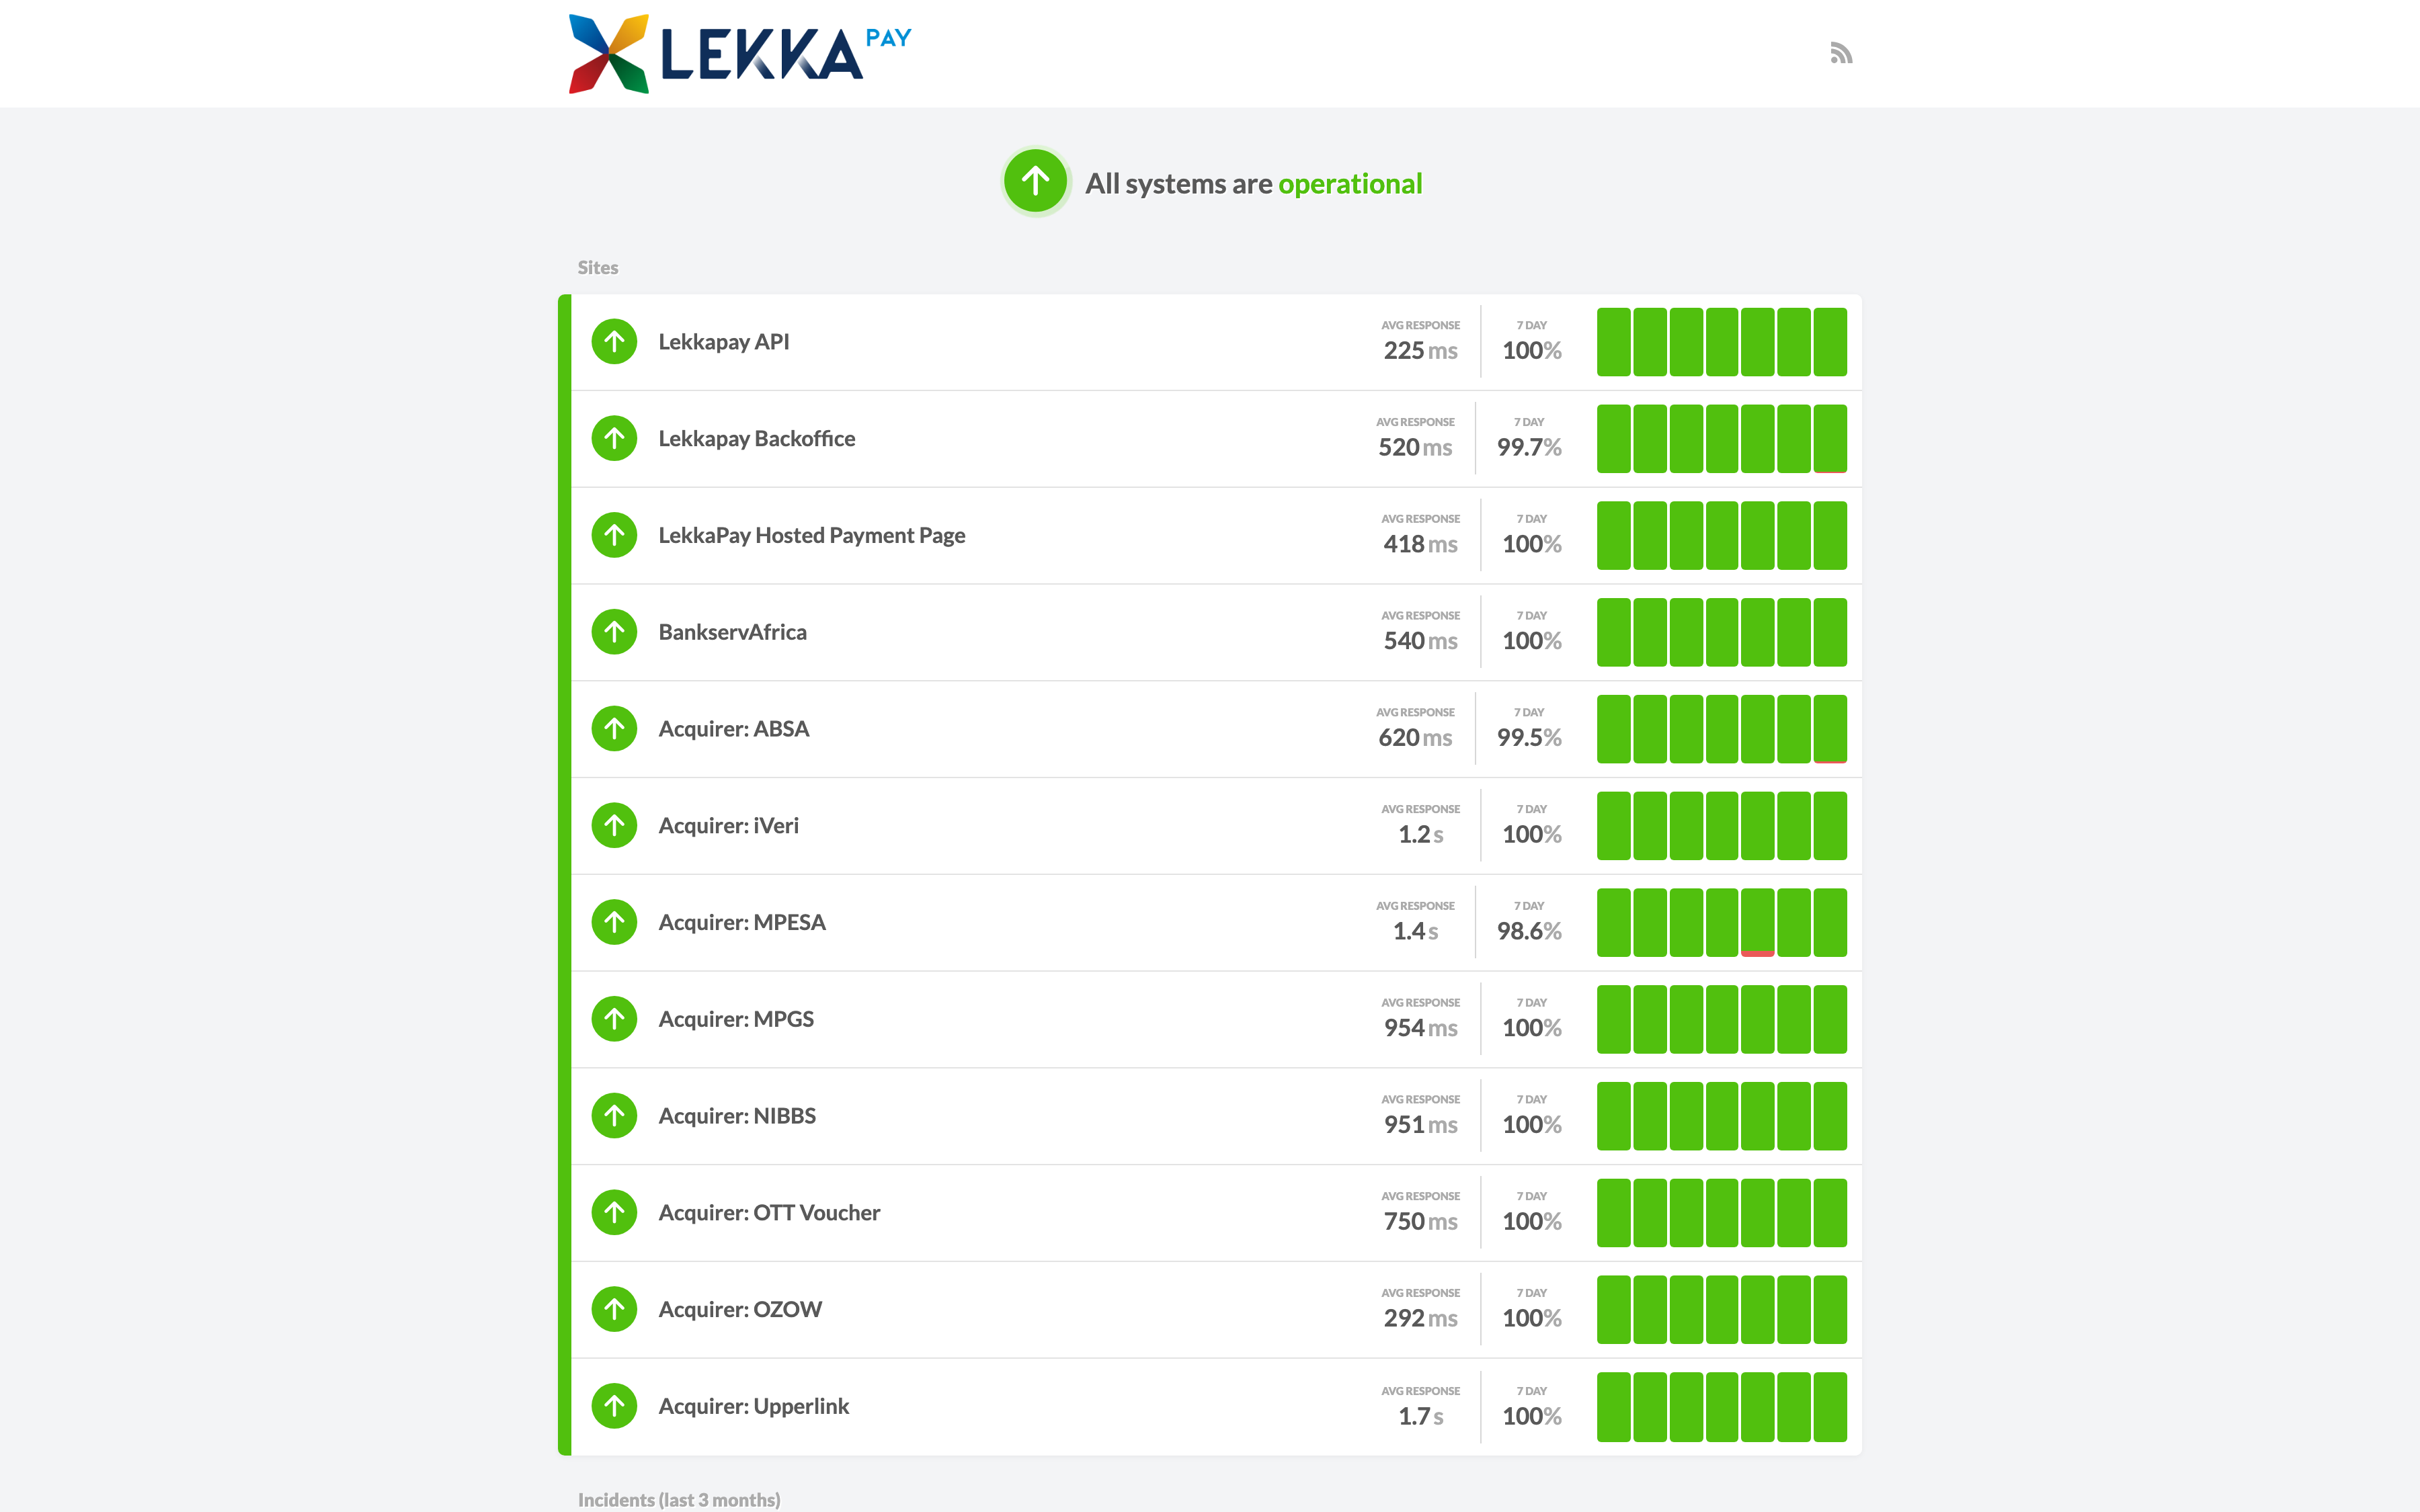
LekkaPay targets 99.999% platform availability, measured over the trailing 12 months - and rather than asking anyone to take a number on trust, we publish live evidence. The public status page at status.lekkapay.com shows current component status, incident history and maintenance notices, and it stays public whether the news is good or bad.
A programme, not a checkbox
Compliance certificates describe a moment; a security programme describes a habit. Ours includes a maintained security policy programme of 24 policies covering the full operational surface, from access control to vendor management, each reviewed on a schedule. We run annual incident-response exercises so that failure is rehearsed before it is real, and every person in the company - not only engineers - completes security awareness training.
Responsible disclosure
If you believe you have found a vulnerability in a LekkaPay system, we want to hear from you, and we will engage in good faith. Report it via the contact page with enough detail to reproduce the issue, and allow us reasonable time to investigate and remediate before any public disclosure. We do not pursue researchers who report responsibly.
Request our compliance pack
Procurement, security and risk teams can request the full compliance pack - PCI DSS attestation of compliance, company registration details, policy summaries and supporting due-diligence documentation - via the contact page. One request, one pack, everything your vendor review needs.
Last updated:
- PCI DSS compliant service provider - the standard's highest level
- Level 1
- PCI Security Standards Council framework
- platform availability
- 99.999%
- Measured platform availability, trailing 12 months
- maintained policies in the security policy programme
- 24
- African Payment Solutions security programme
Uptime
Is LekkaPay up right now?
A public status page with live uptime and response times.
FAQ
Your questions, answered
Is LekkaPay PCI DSS compliant?
Yes. African Payment Solutions, the company behind LekkaPay, is a PCI DSS Level 1 compliant service provider - the highest level of the Payment Card Industry Data Security Standard, validated by independent assessment rather than self-assessment. Merchants using hosted checkout keep card data off their systems entirely.
How is card data stored?
Card numbers are tokenised on arrival and held in an isolated token vault. Merchants and downstream systems work with tokens, never raw card numbers. Data is encrypted in transit and at rest, with encryption keys held in cloud HSM-backed key management.
Is LekkaPay POPIA compliant?
Our processes are aligned with POPIA, South Africa's Protection of Personal Information Act. In plain language: we collect the minimum personal information needed to process payments and meet legal obligations, use it only for those purposes, protect it with the same controls that protect card data, and never sell it.
Can I get compliance documentation for procurement?
Yes. Our compliance pack - PCI DSS attestation, company registration details, policy summaries and due-diligence documentation - is available on request via the contact page.
Where can I check platform status?
At status.lekkapay.com - a public status page with current component status, incident history and maintenance notices. No login required.

Ready when you are.
Apply online in minutes, or talk to us about the right model for your business.